
Private 5G resilience does not come from a cheerful dashboard or a nice radio map. I want to see where the attach failed, which path dropped, and whether the core is quietly spoiling the whole thing; otherwise you are guessing, and guessing is a poor plan when the network is already sulking.
TPM-only BitLocker is convenient, but convenience is not the same as a proper boundary. BitLocker PINs push that line back to pre-boot, which is where...
Ocean Protocol BPool single-sided join exit math is where this one falls apart, and I have a soft spot for bugs that look tidy until another contract...
Lixir Vault permit signatures looked ordinary until the final check was missing. If `ecrecover` only needs to return a nonzero address, you have not...
Composer supply chain attack is one of those phrases that sounds abstract until a normal looking release starts carrying poisoned code. I trust tags less than I used to, because once they move,...
AWS Cognito PreSignUp_ExternalProvider is where the awkward bit starts, because the claim becomes a user record before most of the usual checks wake up. I’ve seen enough homelab messes to know that a...
CFITSIO Extended Filename Syntax is the bit that makes a harmless-looking path dangerous. Once I let untrusted input reach `fits_open_file`, I am no longer passing a filename, I am handing control to...
Stay updated with the latest in tech! This digest covers AI ethics, auto industry shifts, and the impact of politics on technology, exploring today's pressing issues.
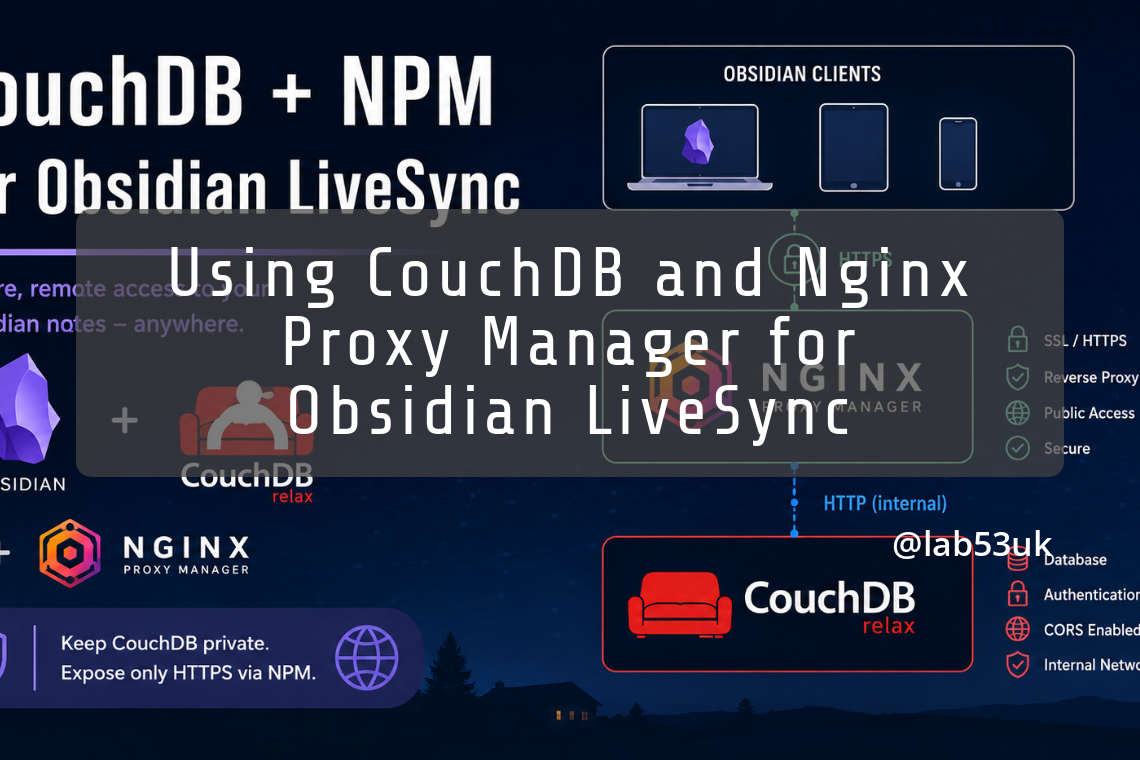
I already had Obsidian LiveSync working inside the local network using the CouchDB IP address and port. That was fine while I was at home or in the office, but it was not enough once I wanted my notes...
Cisco Catalyst SD-WAN authentication bypass is the sort of flaw that turns a controller into an entry point, then a staging area. Once someone has admin-level access without a login, I stop assuming...
large-scale patch releases do not just create risk, they expose how much of your estate is already running on borrowed time. I prefer monitoring that catches odd process chains, strange logins and...
BadIIS is the sort of mess that hides in plain sight, because the site still loads while visitors are quietly sent elsewhere. I look for odd IIS log patterns, stray build artefacts, and service...
OpenVPN vulnerabilities are tedious until they are not; this one lives in the handshake path, so a crafted packet can knock the process over before you have even noticed the client has connected. I...
A third-party development software compromise does not need to reach production to hurt. If a tool can read GitHub files, it can still expose source code, secrets, and enough context to make the next...
