TPM-only BitLocker is tidy until you remember what is left exposed when the machine can unlock itself. BitLocker PINs are the small, awkward step that makes a stolen laptop less cooperative, and I trust that far more than wishful thinking about physical security.
Secure connectivity principles only work when the boundary is real, not decorative. I’ve seen too many remote paths that looked neat on paper and fell...

Private 5G resilience does not come from a cheerful dashboard or a nice radio map. I want to see where the attach failed, which path dropped, and...
TPM-only BitLocker is convenient, but convenience is not the same as a proper boundary. BitLocker PINs push that line back to pre-boot, which is where...
Abuse rarely stays put for long, and a hosting provider abuse problem usually survives because the signals never meet in one place. I have seen enough fleets to know the weak point is not logging, it...
Streaming auth code theft is dull in the way most real abuse is, a few weak joins, a live session, and suddenly the whole thing can be relayed and resold. I keep coming back to the same point, if the...
Composer supply chain attack is one of those phrases that sounds abstract until a normal looking release starts carrying poisoned code. I trust tags less than I used to, because once they move,...
AWS Cognito PreSignUp_ExternalProvider is where the awkward bit starts, because the claim becomes a user record before most of the usual checks wake up. I’ve seen enough homelab messes to know that a...
CFITSIO Extended Filename Syntax is the bit that makes a harmless-looking path dangerous. Once I let untrusted input reach `fits_open_file`, I am no longer passing a filename, I am handing control to...
Stay updated with the latest in tech! This digest covers AI ethics, auto industry shifts, and the impact of politics on technology, exploring today's pressing issues.
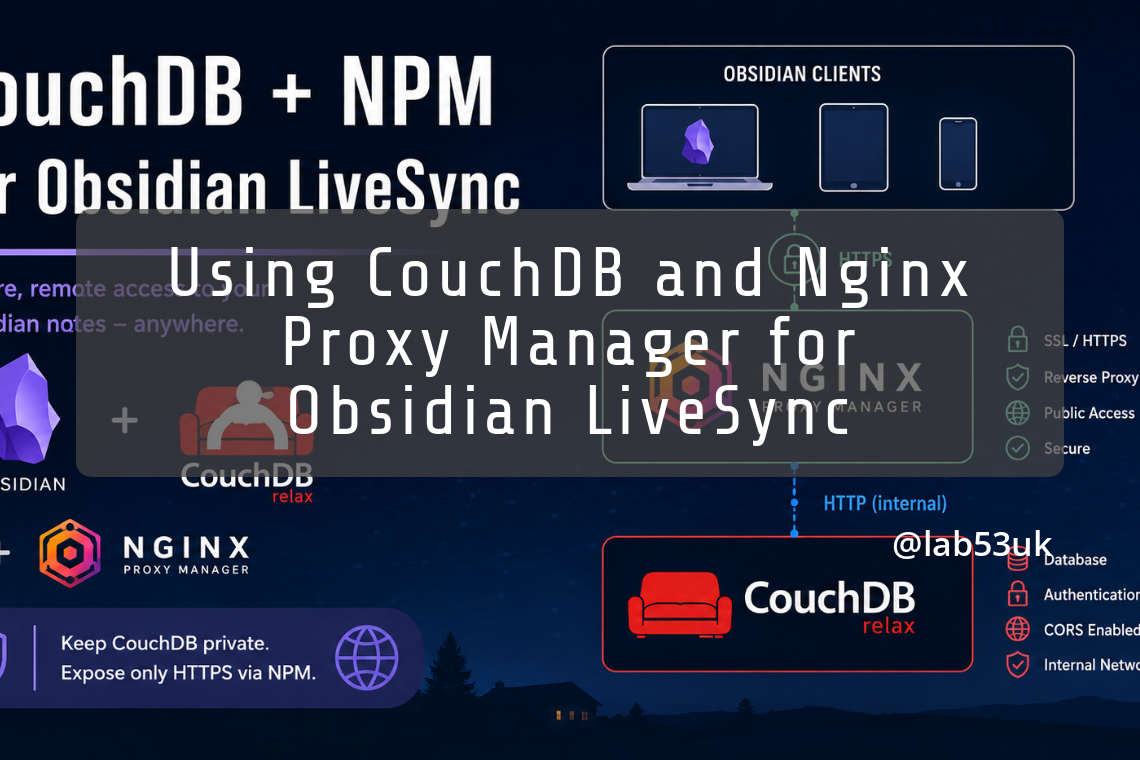
I already had Obsidian LiveSync working inside the local network using the CouchDB IP address and port. That was fine while I was at home or in the office, but it was not enough once I wanted my notes...
Cisco Catalyst SD-WAN authentication bypass is the sort of flaw that turns a controller into an entry point, then a staging area. Once someone has admin-level access without a login, I stop assuming...
large-scale patch releases do not just create risk, they expose how much of your estate is already running on borrowed time. I prefer monitoring that catches odd process chains, strange logins and...
BadIIS is the sort of mess that hides in plain sight, because the site still loads while visitors are quietly sent elsewhere. I look for odd IIS log patterns, stray build artefacts, and service...
