Modified PDF viewers are a neat little delivery trick because they look like ordinary job bait until someone opens them. I keep coming back to the same point, the file name is not the danger, the loader path is; that is where the unwanted code slips in.
Ransomware group fragmentation means the label matters less than the behaviour, and I trust activity over reputation every time. A small crew with...

Linux kernel net/sched use-after-free looks messy on paper, and on CentOS 9 Desktop it is worse, because the obvious paths are blocked and the useful...
Streaming auth code theft is dull in the way most real abuse is, a few weak joins, a live session, and suddenly the whole thing can be relayed and resold. I keep coming back to the same point, if the...
Composer supply chain attack is one of those phrases that sounds abstract until a normal looking release starts carrying poisoned code. I trust tags less than I used to, because once they move,...
AWS Cognito PreSignUp_ExternalProvider is where the awkward bit starts, because the claim becomes a user record before most of the usual checks wake up. I’ve seen enough homelab messes to know that a...
CFITSIO Extended Filename Syntax is the bit that makes a harmless-looking path dangerous. Once I let untrusted input reach `fits_open_file`, I am no longer passing a filename, I am handing control to...
Stay updated with the latest in tech! This digest covers AI ethics, auto industry shifts, and the impact of politics on technology, exploring today's pressing issues.
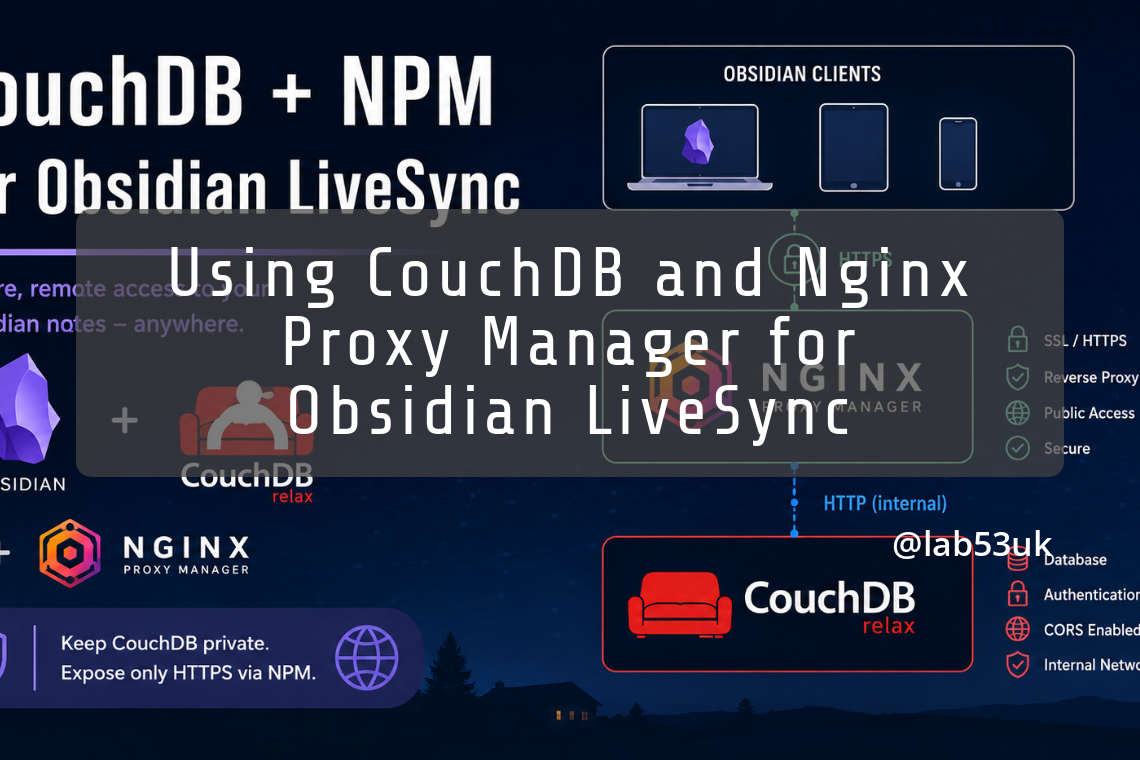
I already had Obsidian LiveSync working inside the local network using the CouchDB IP address and port. That was fine while I was at home or in the office, but it was not enough once I wanted my notes...
Cisco Catalyst SD-WAN authentication bypass is the sort of flaw that turns a controller into an entry point, then a staging area. Once someone has admin-level access without a login, I stop assuming...
large-scale patch releases do not just create risk, they expose how much of your estate is already running on borrowed time. I prefer monitoring that catches odd process chains, strange logins and...
BadIIS is the sort of mess that hides in plain sight, because the site still loads while visitors are quietly sent elsewhere. I look for odd IIS log patterns, stray build artefacts, and service...
OpenVPN vulnerabilities are tedious until they are not; this one lives in the handshake path, so a crafted packet can knock the process over before you have even noticed the client has connected. I...
