
Stay updated with the latest in tech! This digest covers AI ethics, auto industry shifts, and the impact of politics on technology, exploring today's pressing issues.

Cloudflare WAF Managed Rules have a habit of changing underneath you, and old SSRF names can linger long after the protection has gone. I prefer to...
Stay updated with the latest in tech! This digest covers AI ethics, auto industry shifts, and the impact of politics on technology, exploring today's...
Cloudflare WAF WordPress XSS detection now has a cleaner CVE label, but the behaviour has not changed; the rule still blocks the same traffic, just...
Trend Micro Apex One zero-day is not the sort of bug you shrug off, because the server-side flaw lets a compromised admin box start pushing code to trusted agents. If you run Apex One on Windows, the...
Call-tracking data is useful until it is not, and tech support fraud knows that better than most. Rotate enough numbers, split the complaints, and the abuse starts to look like ordinary churn, which...
Abuse rarely stays put for long, and a hosting provider abuse problem usually survives because the signals never meet in one place. I have seen enough fleets to know the weak point is not logging, it...
Streaming auth code theft is dull in the way most real abuse is, a few weak joins, a live session, and suddenly the whole thing can be relayed and resold. I keep coming back to the same point, if the...
Composer supply chain attack is one of those phrases that sounds abstract until a normal looking release starts carrying poisoned code. I trust tags less than I used to, because once they move,...
AWS Cognito PreSignUp_ExternalProvider is where the awkward bit starts, because the claim becomes a user record before most of the usual checks wake up. I’ve seen enough homelab messes to know that a...
CFITSIO Extended Filename Syntax is the bit that makes a harmless-looking path dangerous. Once I let untrusted input reach `fits_open_file`, I am no longer passing a filename, I am handing control to...
Stay updated with the latest in tech! This digest covers AI ethics, auto industry shifts, and the impact of politics on technology, exploring today's pressing issues.
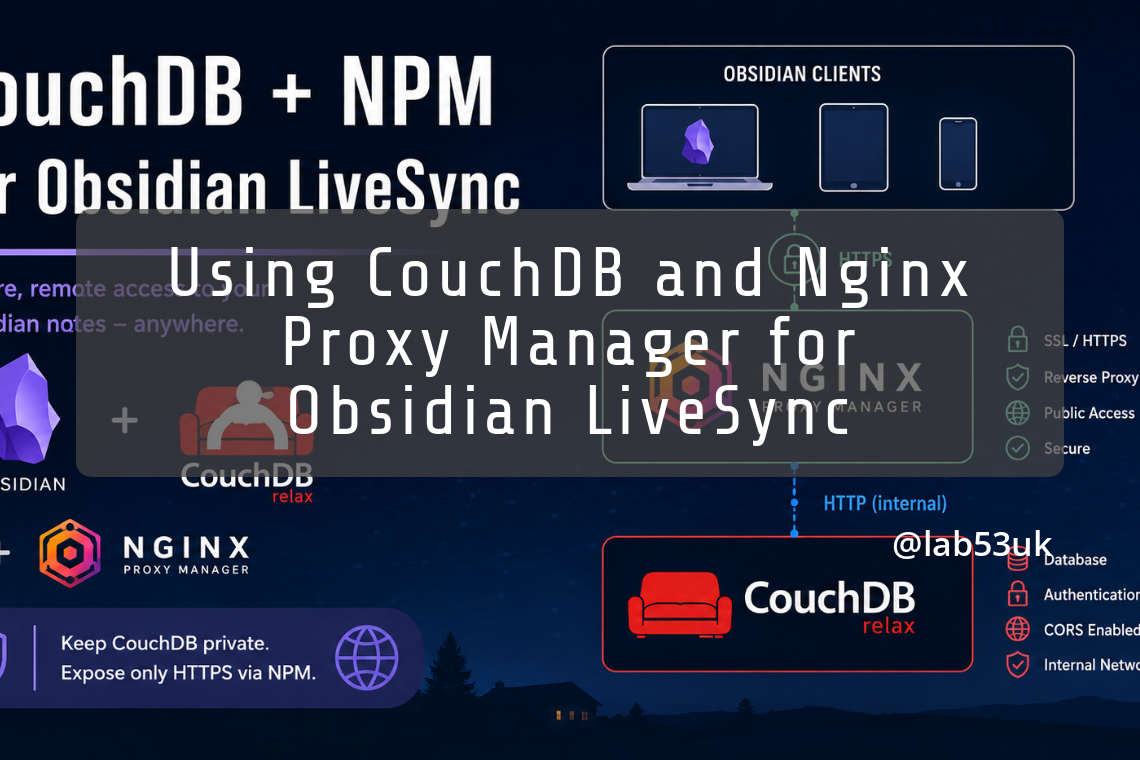
I already had Obsidian LiveSync working inside the local network using the CouchDB IP address and port. That was fine while I was at home or in the office, but it was not enough once I wanted my notes...
Cisco Catalyst SD-WAN authentication bypass is the sort of flaw that turns a controller into an entry point, then a staging area. Once someone has admin-level access without a login, I stop assuming...
